Assessment records
Every control answer keeps its assessor, its date and the material behind it.
We built ComplianceVault for teams working through Qatar's National Information Assurance Policy. It starts where the policy starts, with the business processes that matter and the information they depend on, and uses that to decide how many controls you actually owe before a single one is assessed.
 AzbersInnovations
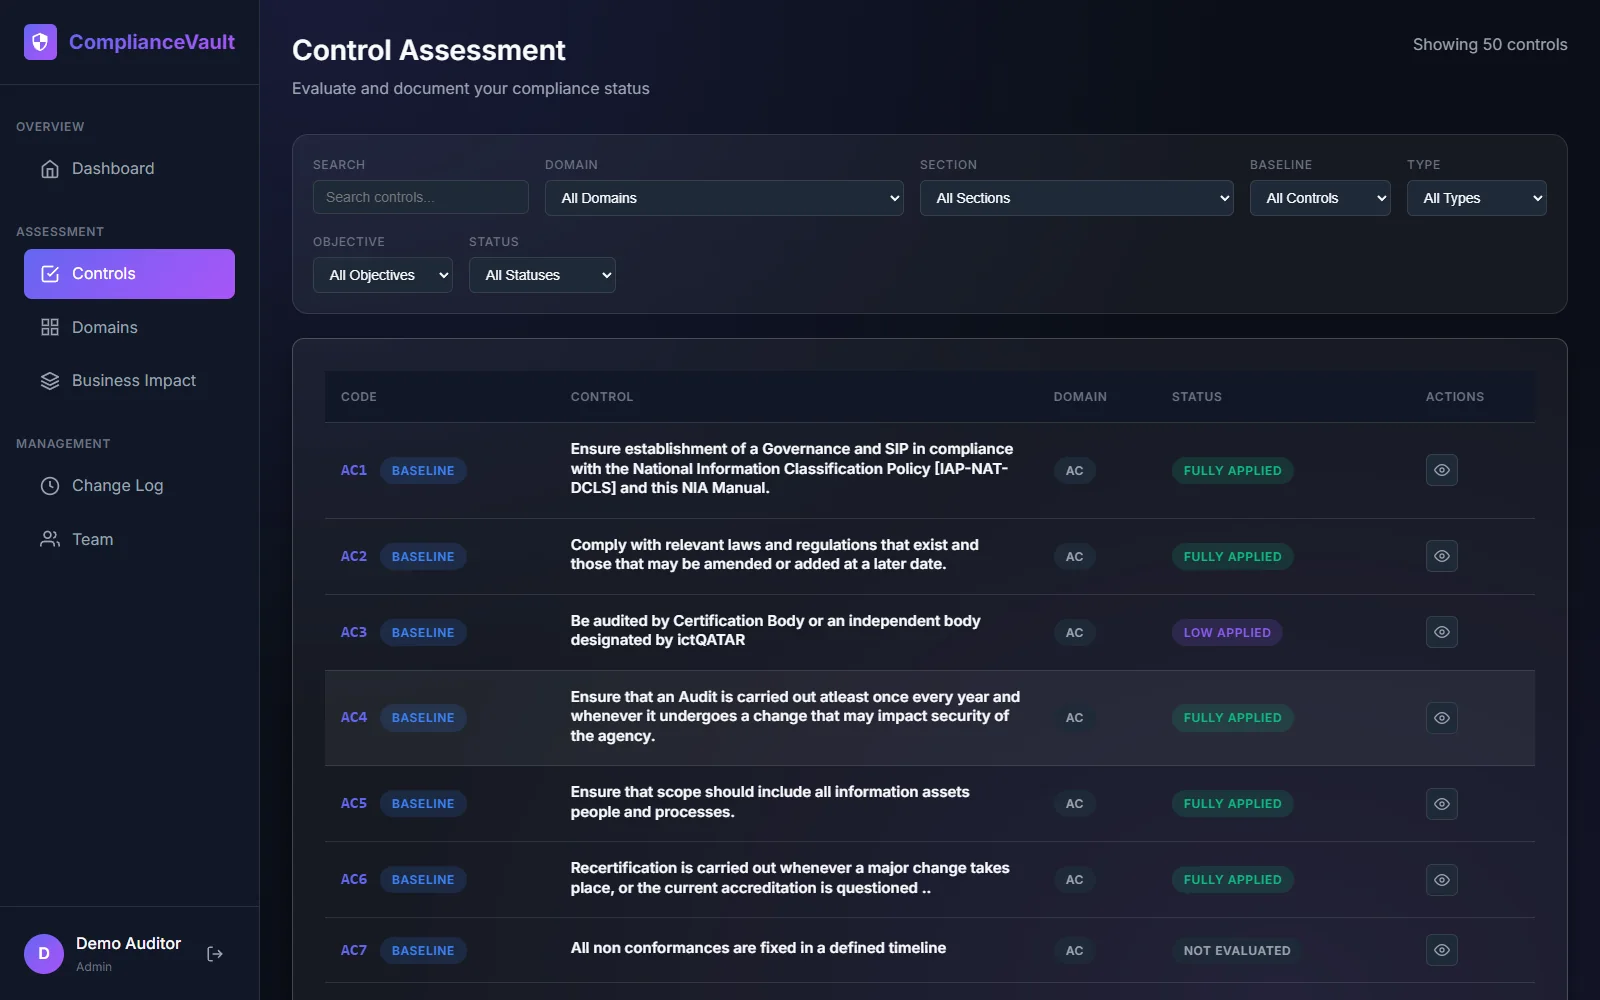
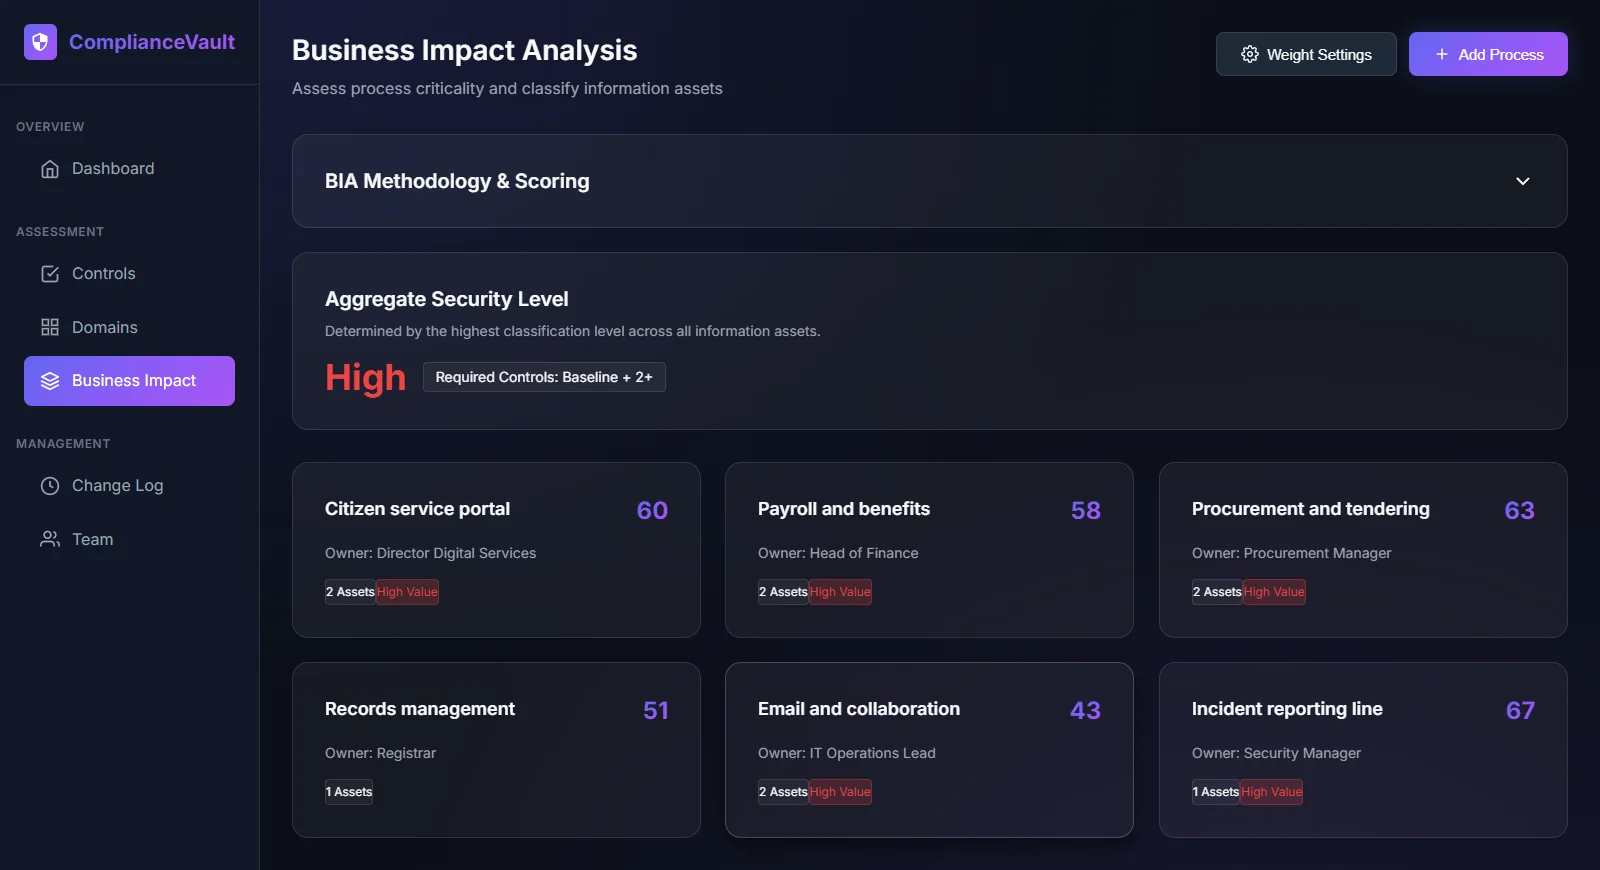
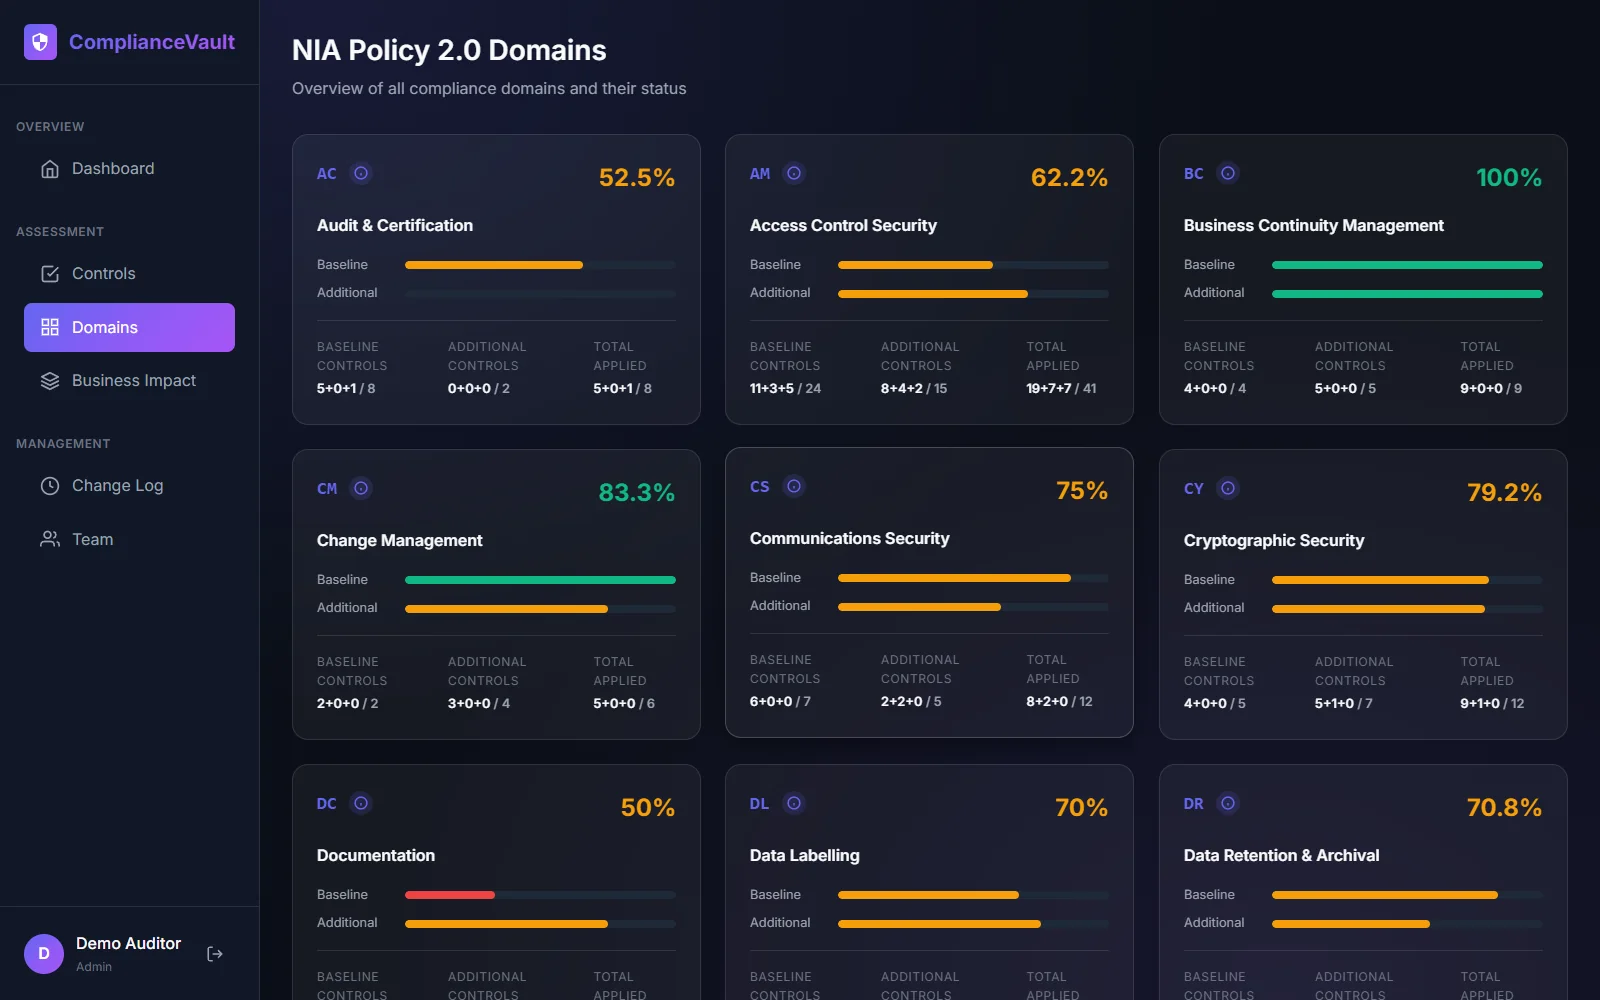
Screens from a ComplianceVault instance loaded with a sample agency. The processes, assets and results are sample data.
Most teams begin at the control list, which is the wrong end. Until you know which processes cannot stop and which information needs the most protection, choosing controls is guesswork with a template attached. ComplianceVault holds the order the policy expects.
Score each process on reputation, external, internal, legal and economic impact.
Rate each asset for confidentiality, integrity and availability.
The highest rating sets the security level, and the level sets the controls owed.
Fully, partially, lightly or not applied, with the reasoning kept.
Files stay with the control they justify, not in a shared folder.
Every change is logged, so the history explains the current state.
An agency whose information is all low impact owes the baseline controls. One with a single high impact asset owes the baseline plus two more controls in every domain. ComplianceVault works that out from the ratings you give your assets and moves the target the moment a rating changes, so nobody discovers at audit that the goalposts were in the wrong place.
 AzbersInnovations
Each domain shows baseline and additional controls separately, so a strong result on the easy half cannot hide a gap in the half the security level added. The weakest domain is obvious at a glance, which is where the next month of work should go.
 AzbersInnovations
ComplianceVault knows one policy well rather than many loosely, which is what a team in the middle of a NIA programme needs from it. It came out of our own delivery work and we still use it on engagements.
Where an organisation answers to more than one framework, the mapping problem is the one ControlGraph is built for. For Pakistan's national framework, CyberNexus carries assessment through to certification.
Every control answer keeps its assessor, its date and the material behind it.
Each NIA control shows where it meets ISO 27001, PCI DSS and NIST SP 800-53.
Every edit is recorded with who made it and when.
The submission comes from the same records the team worked in all year.
The questions that come up most often, answered the way we would answer them on a call.
Yes, deliberately. It holds the NIA Policy 2.0 controls with their cross references and follows the order the policy expects. Organisations answering to several frameworks at once are usually a better fit for ControlGraph.
They serve different frameworks. ComplianceVault carries a Qatar NIA programme from impact analysis to audit day. CyberNexus is built for Pakistan's framework, with an Authority portal for national review and certification.
Most people do. Tell us which stage is currently stuck, because that is usually a more useful starting point than the beginning.
It stays linked to the control it justifies rather than sitting in a folder near it, and it stays under the same isolation and access rules as everything else we build.
Tell us where you are in it. The useful conversation usually starts with whichever stage is currently stuck, and we can show you that stage in the product.